

Indian Researchers Used Claude To Hack OpenAI In Under 72 Hours, Earned Rs 6 Lakh Bounty
Three Indian-origin cybersecurity researchers have demonstrated how artificial intelligence can dramatically accelerate security research after using Anthropic’s Claude to exploit vulnerabilities in OpenAI’s systems.
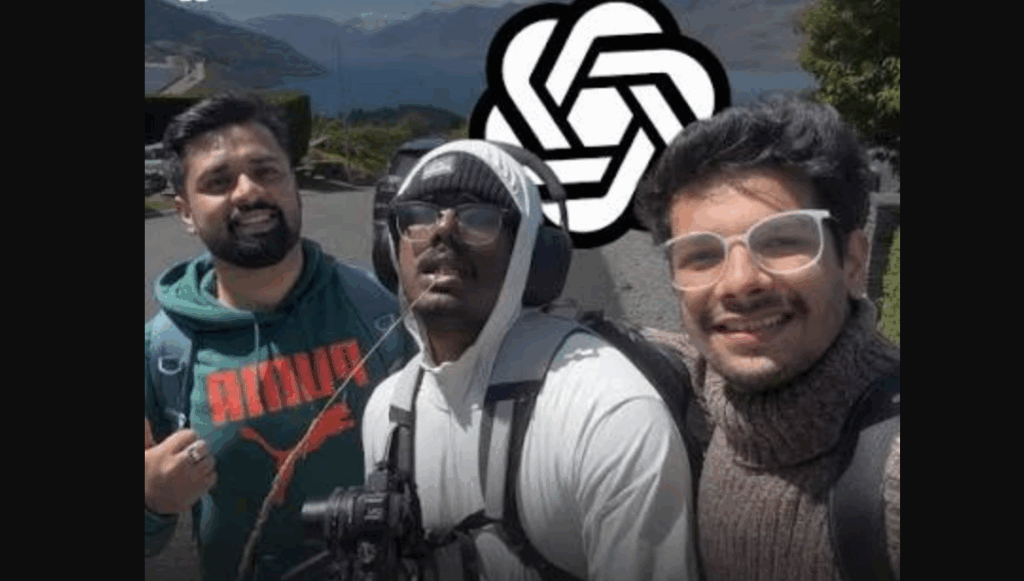
The researchers, from cybersecurity startup Hacktron AI, gained access to several OpenAI employees’ ChatGPT and Codex accounts and eventually reached the company’s private GitHub environment. The exercise was conducted under OpenAI’s bug-bounty programme, making it an authorised security test rather than an unauthorised cyberattack.
Meet The Three Researchers
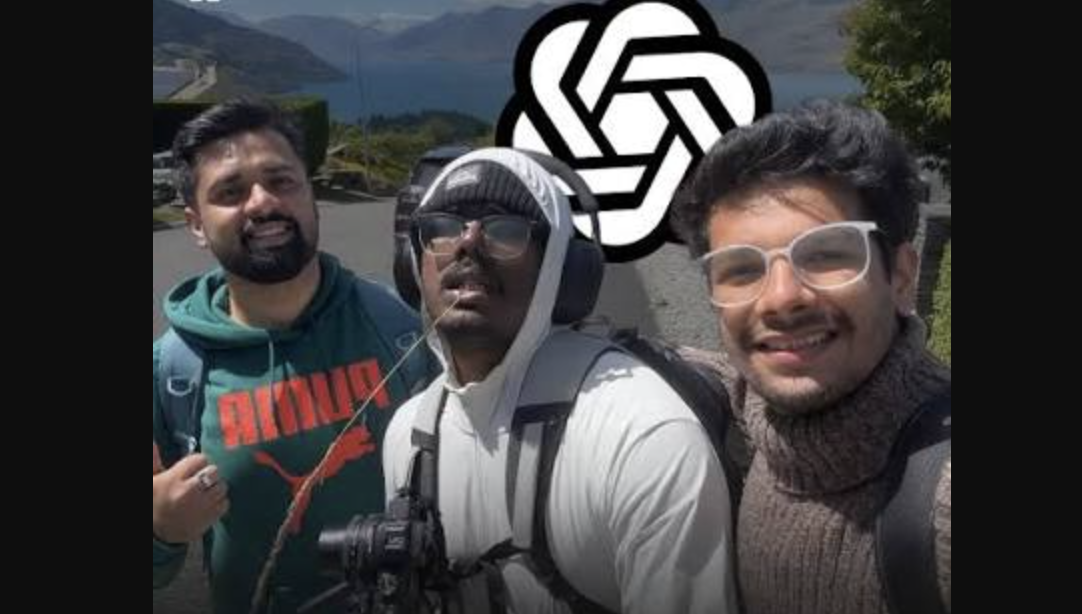
The team consisted of Harsh Jaiswal, Mohan Pedhapati and Rahul Maini, all associated with Hacktron AI.
The researchers have backgrounds in vulnerability research, penetration testing and bug-bounty programmes. Their experience in identifying software weaknesses played an important role in the investigation.
The research was led by Jaiswal, with Pedhapati and Maini working alongside him.
Claude Helped Turn A Vulnerability Into An Exploit
The investigation began with a vulnerability involving OpenAI’s public community forum, which was hosted on the Discourse platform.
The researchers discovered that a flaw involving the processing of certain image files could potentially allow code execution on the forum’s server.
They used Claude to help investigate the vulnerability and develop an exploit. The AI assisted with writing, debugging and adapting parts of the code.
The researchers initially struggled to get a working exploit using an earlier version of Claude. After a newer Claude model became available, the system was reportedly able to produce a successful exploit much faster.
The Attack Chain Went Further
After gaining access to the vulnerable system, the researchers discovered another security weakness involving authentication tokens.
This allowed them to gain access to multiple OpenAI employee ChatGPT and Codex accounts.
One of those accounts was connected to OpenAI’s private GitHub environment. The researchers were therefore able to reach an internal software repository through the compromised employee account.
To demonstrate the extent of their access, they created a harmless pull request that modified a documentation file. The proposed change was not accepted.
The researchers said they stopped their testing after establishing that sensitive internal material could potentially be accessed.
They Did Not Steal OpenAI’s Source Code
Despite headlines describing the incident as an OpenAI hack, there is an important distinction.
The researchers said they did not read or download OpenAI’s private source code. Their objective was to demonstrate the security weaknesses and report them to OpenAI through its bug-bounty programme.
OpenAI subsequently fixed the vulnerabilities, revoked affected authentication tokens and sessions, and tightened permissions.
OpenAI Paid A Rs 6 Lakh Bounty
The researchers were rewarded by OpenAI for identifying and responsibly reporting the vulnerabilities.
The company paid Hacktron AI a bug bounty of $6,500, which is roughly Rs 6 lakh.
The entire investigation reportedly took less than 72 hours from the initial discovery to reaching the internal GitHub environment.
The researchers also spent less than $3,000 on AI tokens during the exercise.
AI Is Changing Cybersecurity
The incident highlights how AI can dramatically reduce the time required for complex cybersecurity research.
However, Claude did not independently decide to attack OpenAI. The researchers found the vulnerabilities, determined how the weaknesses could be connected and controlled the investigation.
AI essentially acted as a powerful assistant for experienced security researchers.
That distinction is becoming increasingly important as AI tools become capable of writing code, debugging exploits and analysing complex technical problems.
A Warning For Companies Using AI
The incident also demonstrates why companies need to treat AI-assisted attacks as a growing cybersecurity concern.
Attackers with relatively limited resources could potentially use AI to accelerate vulnerability discovery and exploitation. At the same time, security teams can use the same technology to identify weaknesses and strengthen defences.
For OpenAI, the Hacktron investigation provided an opportunity to fix vulnerabilities before they could potentially be exploited by malicious actors.
For the wider technology industry, it offers another indication that the speed of cybersecurity attacks and defence could increasingly be determined by how effectively humans use AI.
Summary
Three Indian-origin researchers from Hacktron AI used Anthropic’s Claude to help exploit vulnerabilities in OpenAI’s systems during an authorised security test. They gained access to employee ChatGPT and Codex accounts and reached OpenAI’s private GitHub environment without downloading source code. OpenAI fixed the vulnerabilities and paid the researchers a $6,500 bug bounty after they reported their findings.